Payy Halts Network After $1.92M USDC Drained from Ethereum Rollup
Payy paused its payments platform after roughly $1.92M in USDC was drained from its Ethereum rollup contract.

By Anmol BillaSenior Analyst
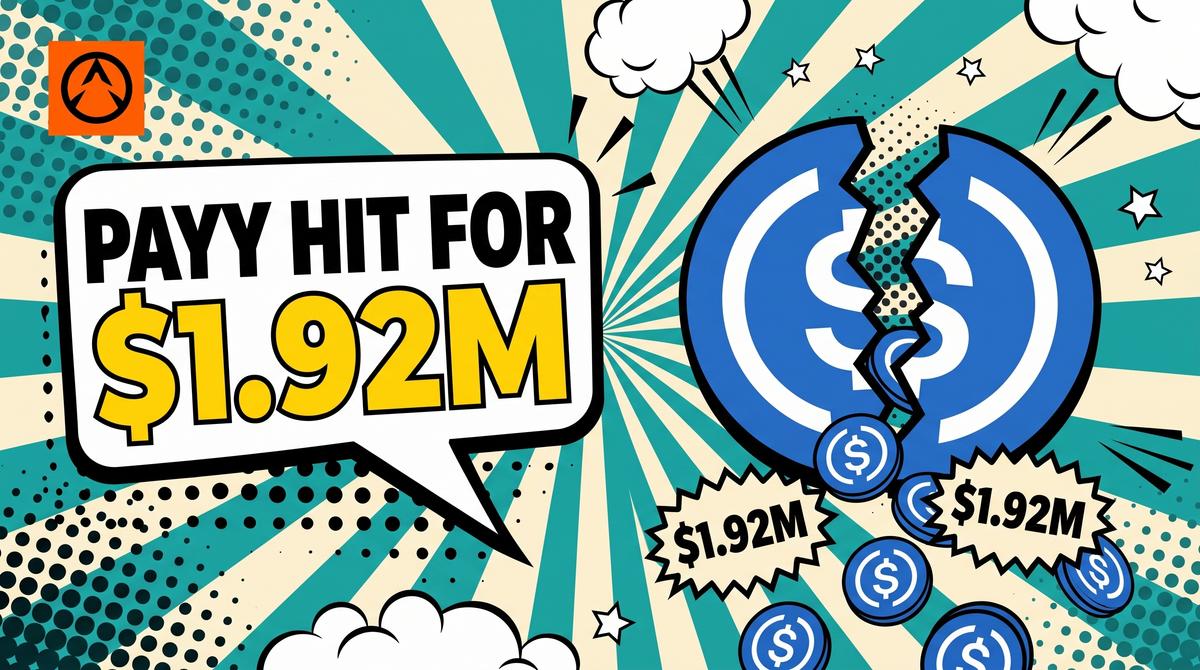
Payy Network shut down its payments platform on September 24 after an attacker drained roughly $1.92 million in USDC from a vulnerability in the project's Ethereum rollup contract. The exploit was carried out through a single malicious transaction that passed through the contract's verifyRollup function, the mechanism the rollup uses to confirm batches of off-chain activity on Ethereum.
What changes for you: if you held funds inside Payy, deposits, withdrawals and card payments are all paused. Payy has not said when the network will reopen, and the company has not committed to making affected users whole.
The drain was confirmed at Ethereum block 26044909 at 04:21 UTC. By crafting a transaction that passed through verifyRollup, the attacker was able to extract USDC that should have remained locked in the contract. The stolen stablecoins were then converted into roughly 683 ETH and fanned out across multiple wallets, with most of the ETH landing in three addresses.
Blockchain investigation firm Specter Investigation traced the stolen funds through the Railgun privacy protocol, a tool that obscures the trail of deposited assets. Whether any of the funds can be recovered from Railgun is not known.
Payy confirmed the attack publicly and said all network operations were suspended while the team works with law enforcement and cybersecurity professionals. The company has not indicated whether affected users will be made whole from its reserves.
This is not Payy's first close call with its own cryptography. In June 2026 the project disclosed a critical flaw in its zk-circuit logic, the layer that produces the zero-knowledge proofs underpinning the platform's privacy features. That earlier bug could have allowed forged burn messages. The team patched it in version 1.3.0 before any funds were lost.
No restart date has been announced.
Anmol Billa
Anmol Billa is a Senior Analyst at Altcoin Buzz, with over five years of experience working across cryptocurrency markets and the broader digital asset industry. His work focuses on technical analysis, market research, investment insights, and evaluating emerging opportunities within the crypto ecosystem. At Altcoin Buzz, Anmol contributes to technical market analysis, research-driven insights, pitch decks, and funding-related initiatives. His experience combines analytical thinking with a practical understanding of crypto markets, helping translate market trends and emerging projects into clear, actionable insights for readers and industry stakeholders.
More from AnmolNext up
Moonwell cbBTC Supplier Asks for Repayment Plan as Cash Runs Dry
A Moonwell supplier wants a repayment plan for the Base cbBTC market, where 93.5% of debt is insolvent and utilization has hit 100% since the MAMO exploit.
 BTC
Related
More in Crypto NewsRelated
BitMart Founder Flags 'Severely Understaffed' Security After New Hack
BTC ETH
Bitcoin Rebounds Above $78,000 as Ethereum Shows Signs of a Trend Reversal
BTCETH
Justin Drake Eyes 2028 for Ethereum's Post-Quantum Shift, a Year Early
ETH
Aztec Tierra Upgrade Patches Critical V5 Flaw and Doubles Proof Speed
ETH